English
 Bahasa Indonesia


 MindSOC capabilities
SOAR
Automated investigation and response workflows, with execution still under your control
 The Problem
Enterprise SOCs face thousands of alerts, mostly false positives. Analysts filter noise while shift changes can reduce coverage
 Features
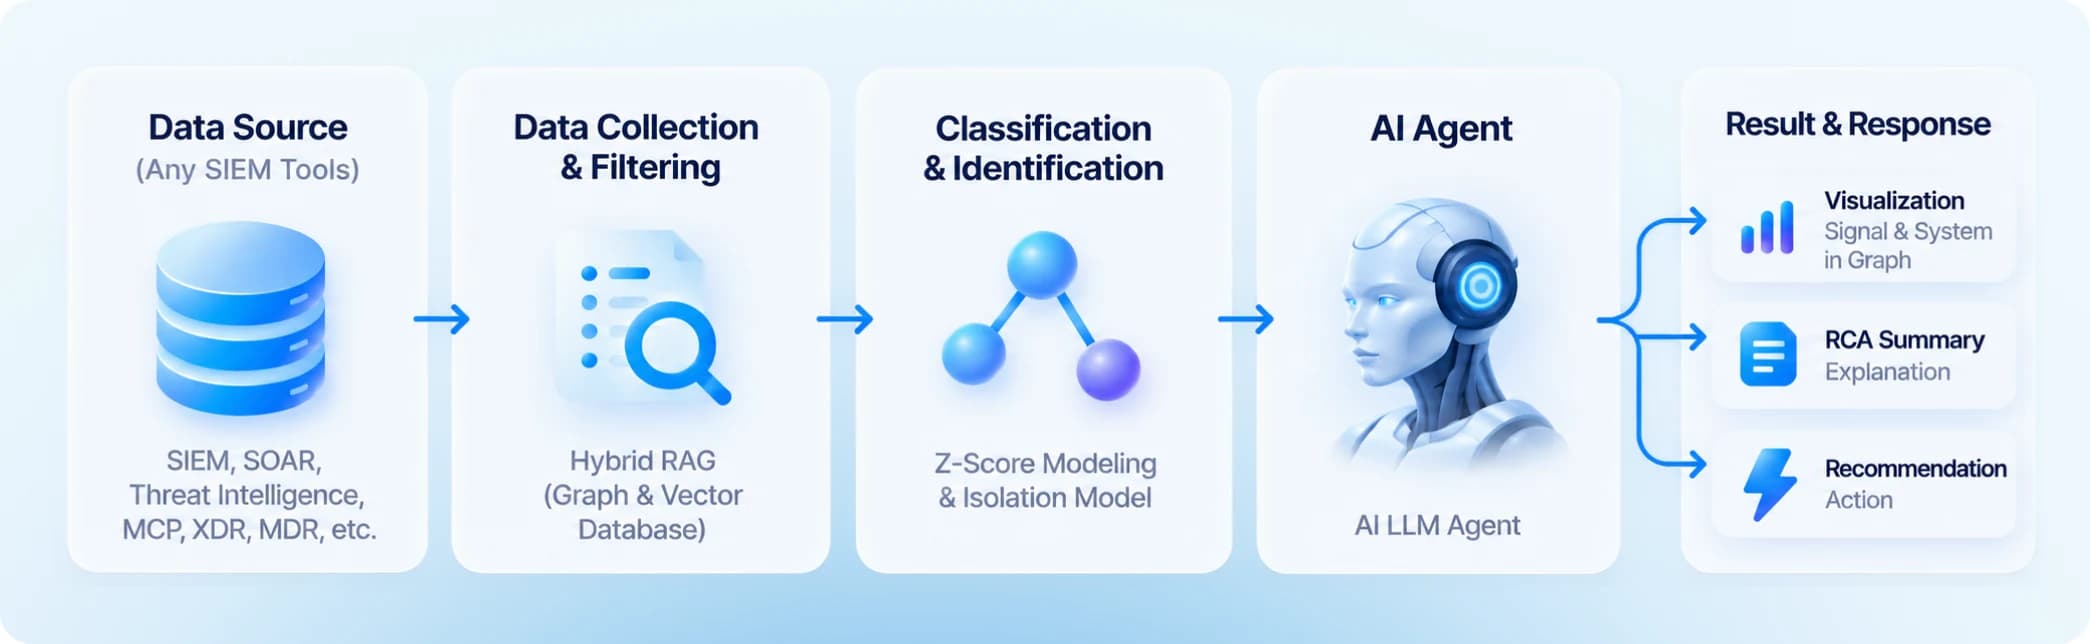
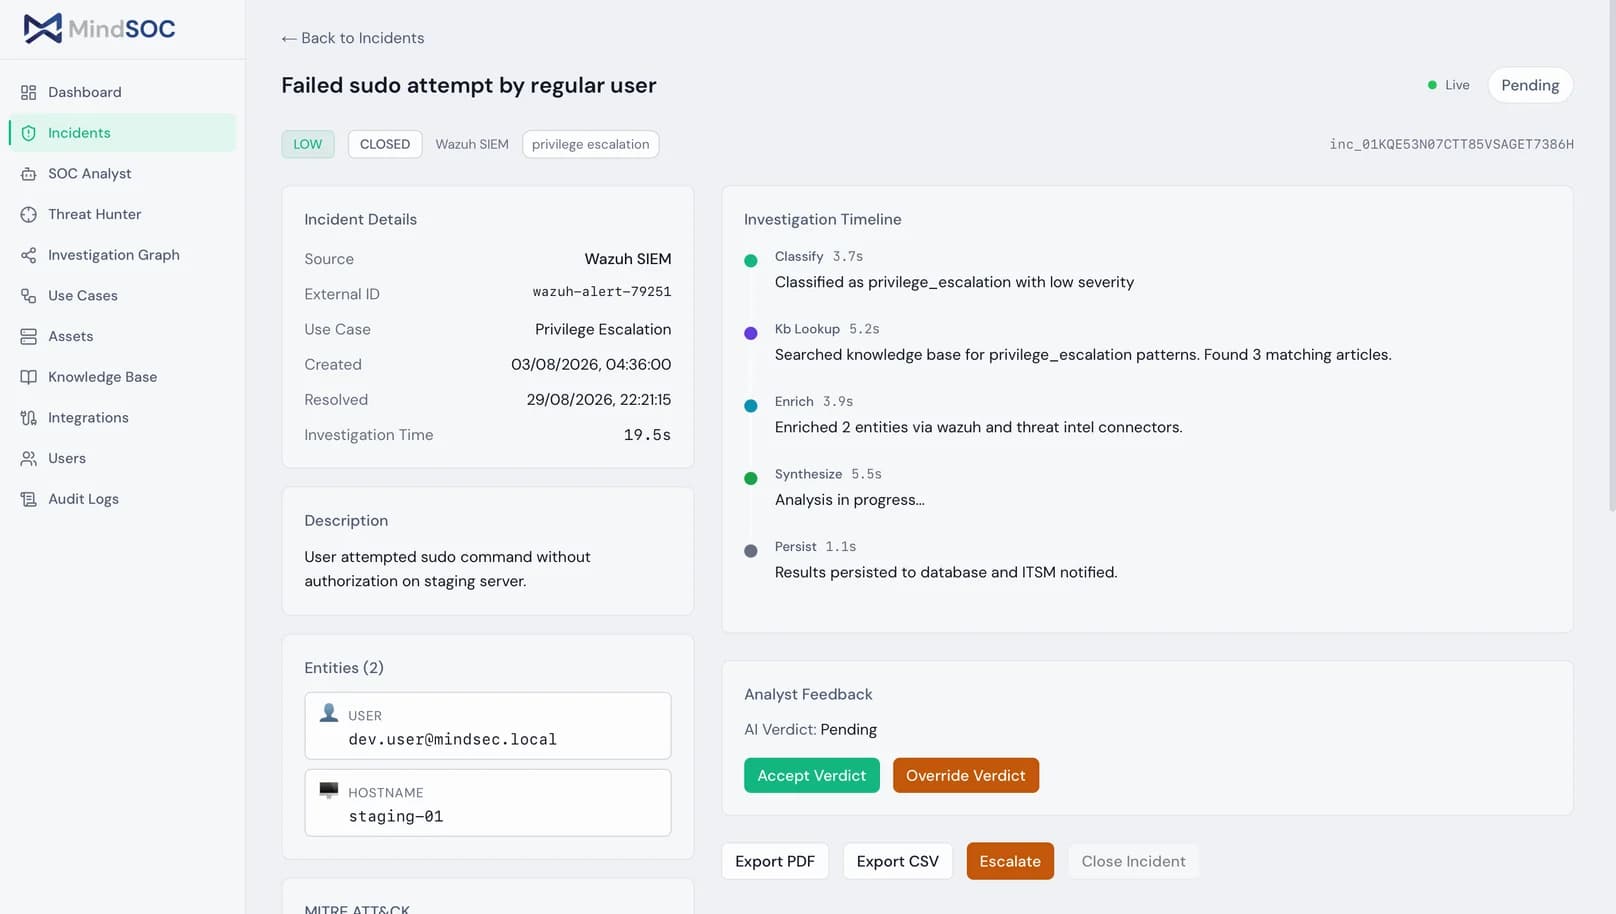
- Five-stage AI investigation pipeline with MITRE ATT&CK mapping
- False positives auto-closed, real threats auto-escalated
- Verdicts written back to Jira, with human approval on high-risk calls
 How It Works
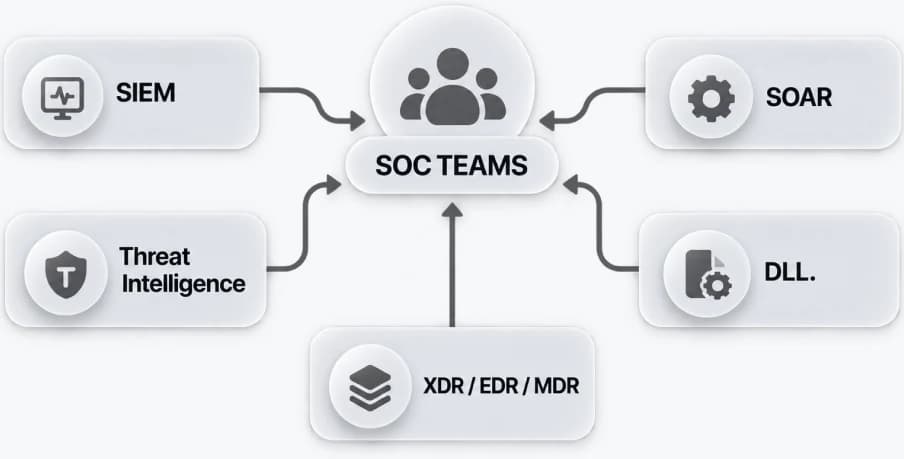
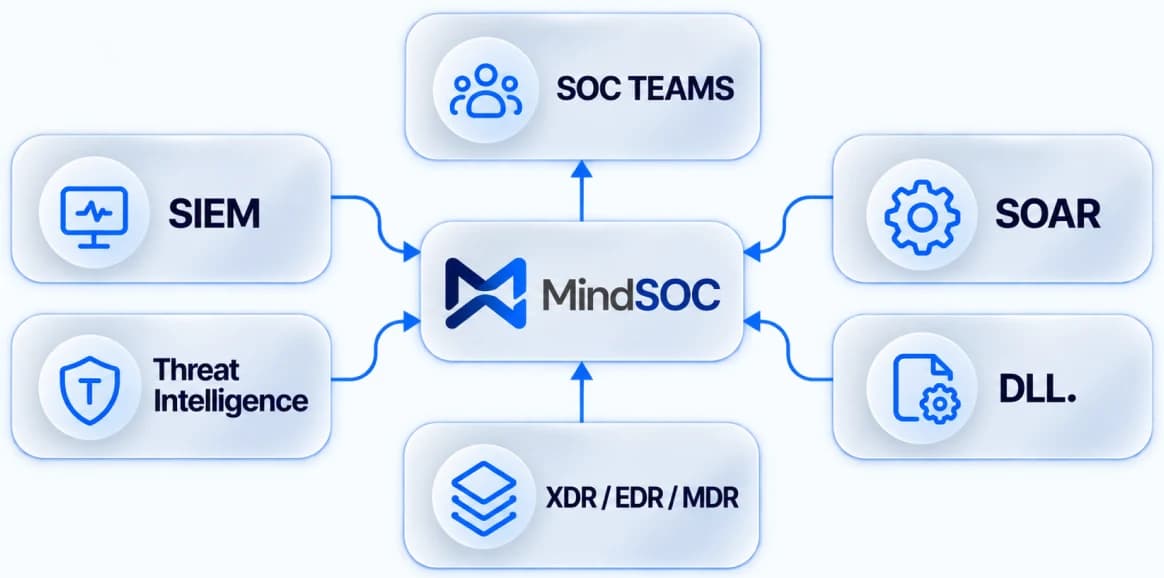
Alerts from SIEM, EDR, WAF and identity tools are classified, enriched with threat intel, mapped into an investigation graph, and returned with evidence in minutes
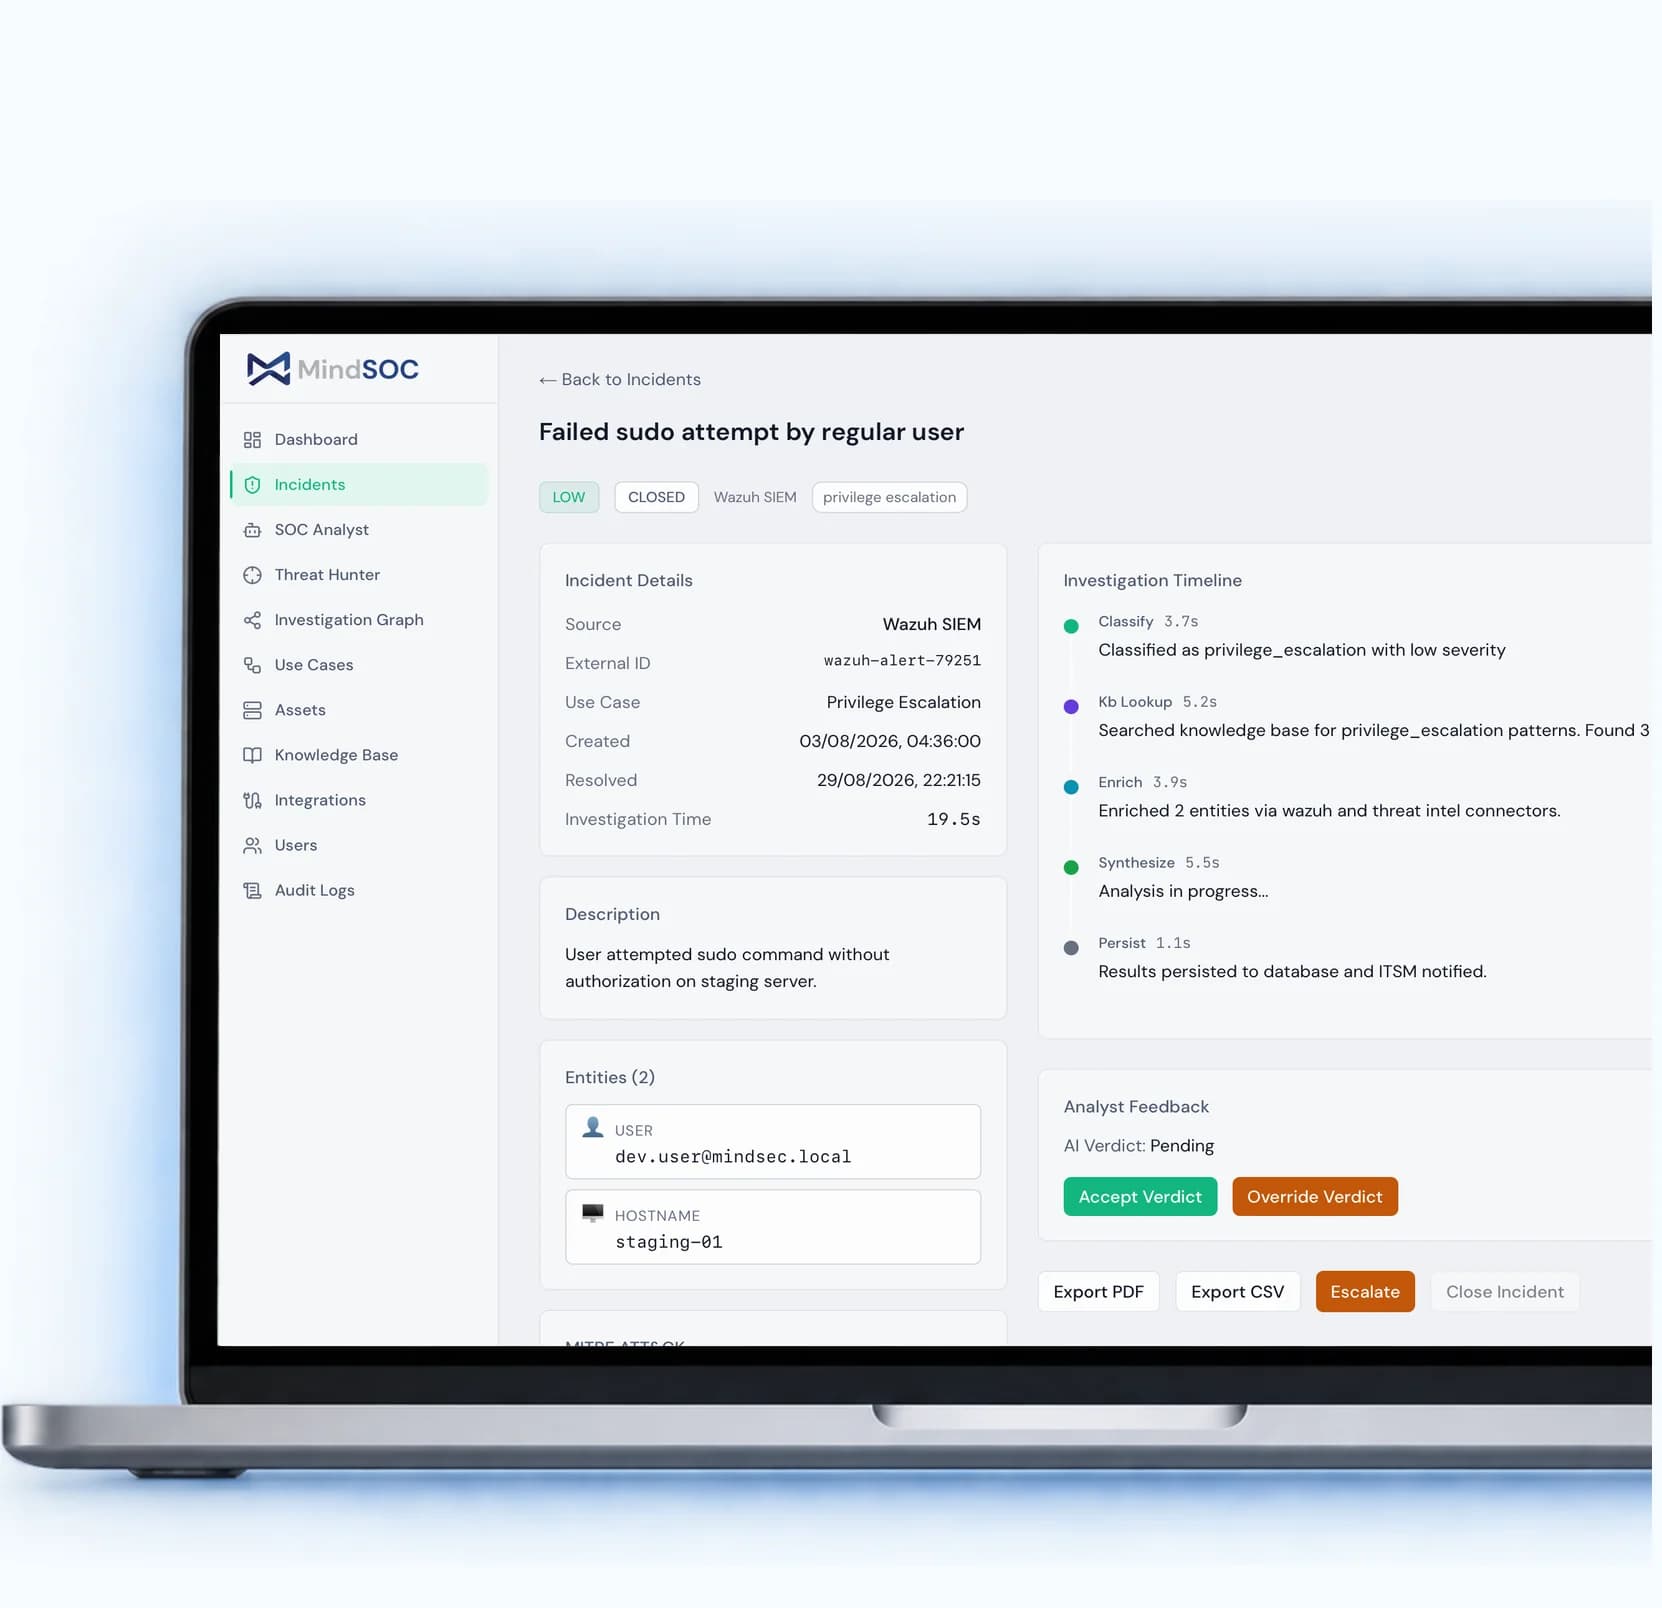




 Auto-categorized threat tracing & escalation
 Analyze all systems simultaneously
 Combine SOC expertise with AI intelligence
 Proactively detect issues before impact