English
 Bahasa Indonesia

 MindSOC capabilities
SOAR
Automated investigation and response workflow, with the execution button still in your hands
 The Problem
Enterprise SOCs face thousands of alerts, mostly false positives. Analysts filter noise while shift changes can reduce coverage
 Features
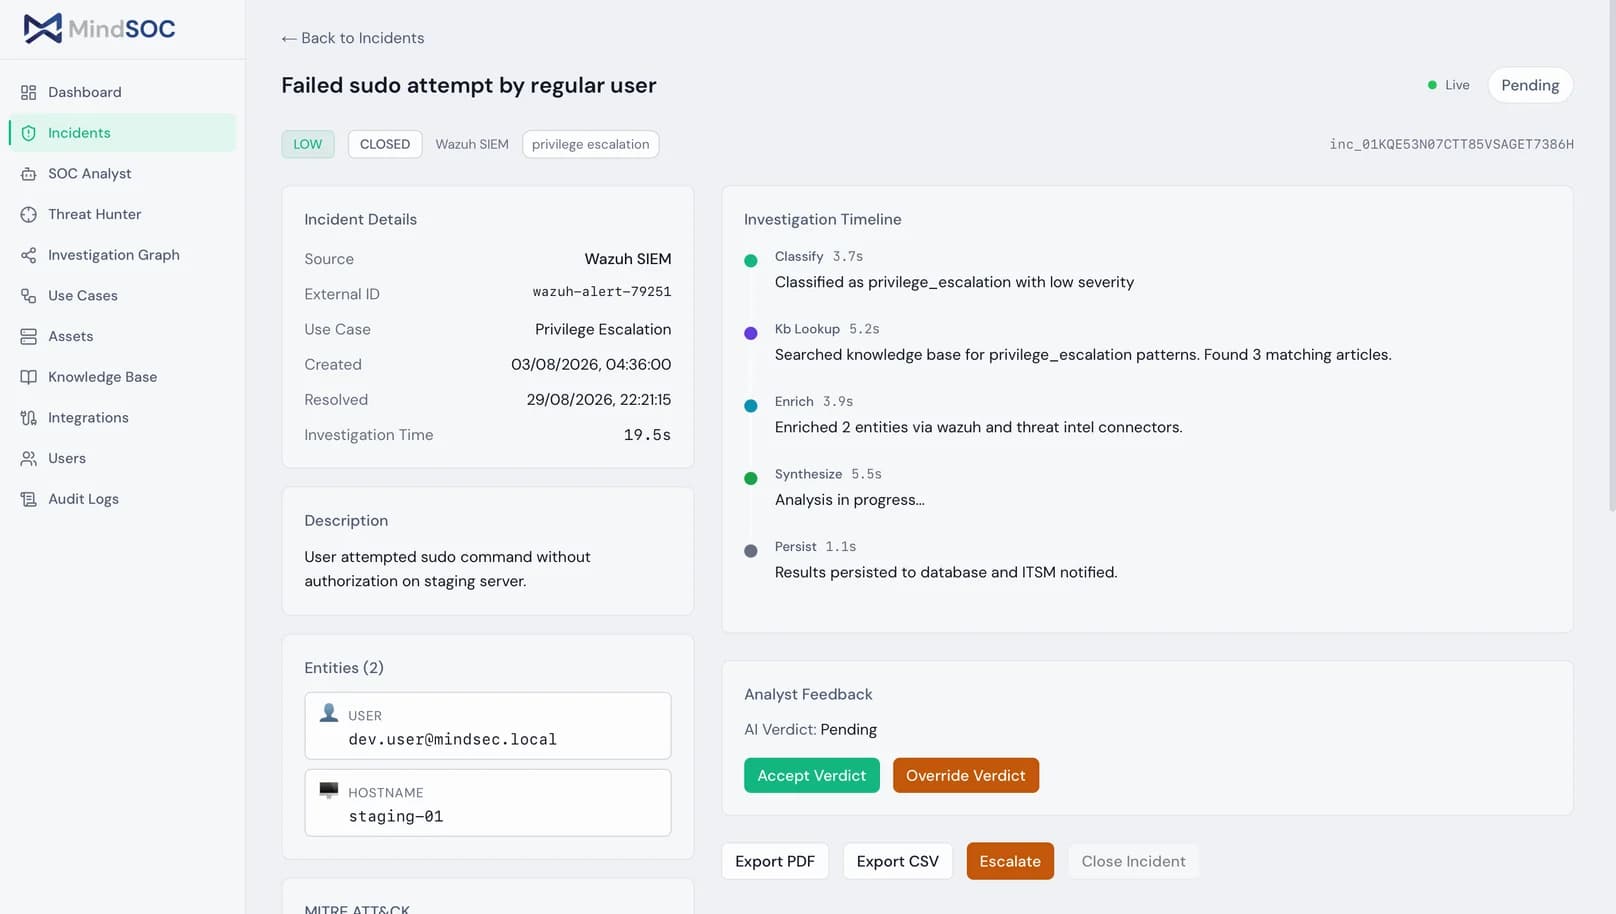
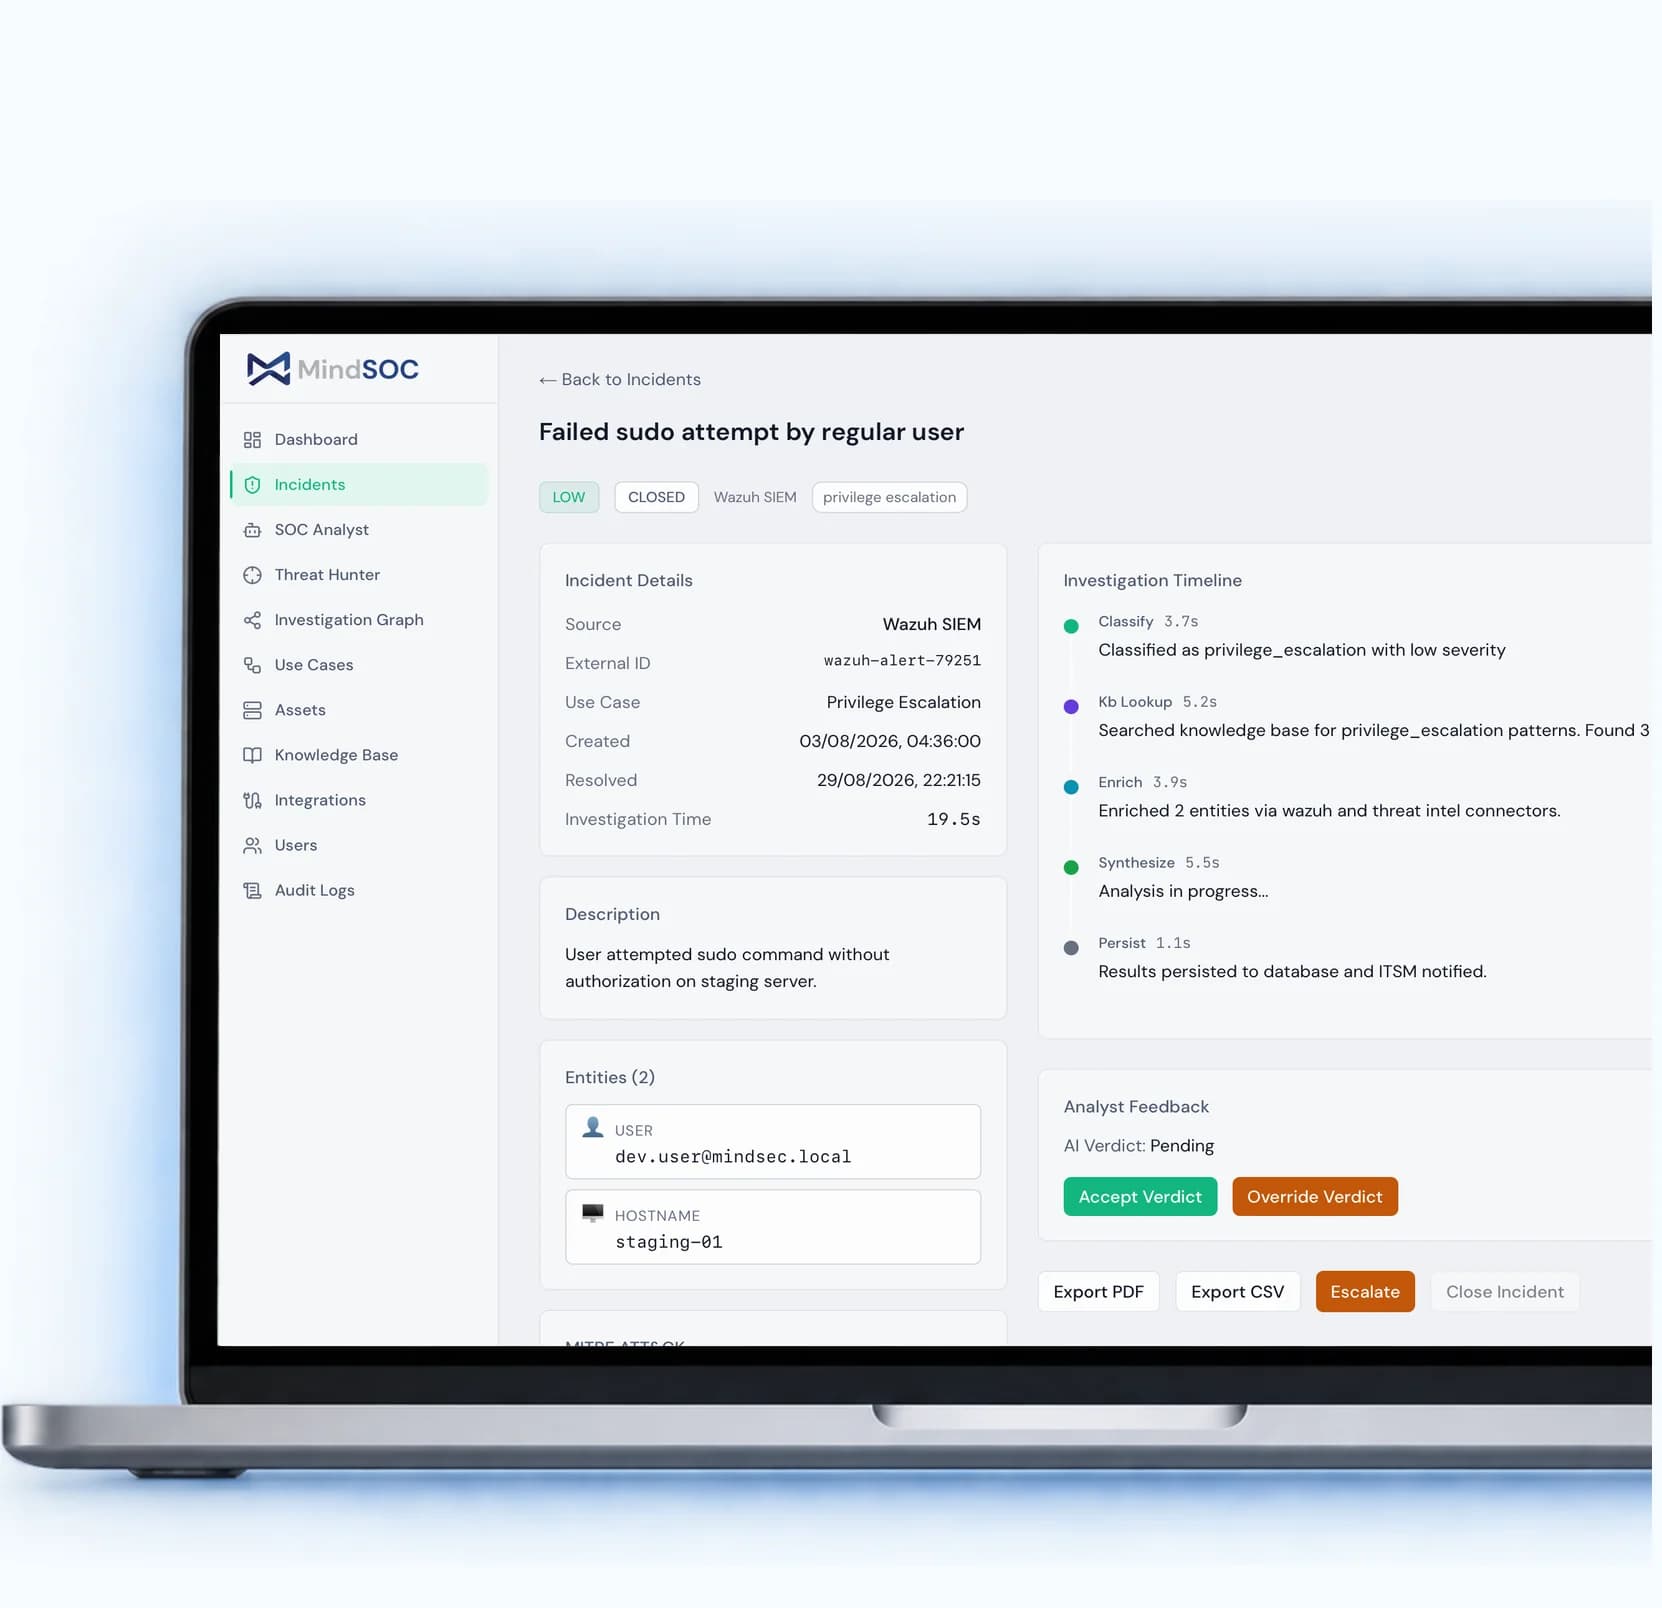
- 5 stage AI investigation pipeline with MITRE ATT&CK mapping
- Auto-close for false positives, auto-escalate for real ones
- Verdicts written back to Jira, with human approval on high-risk calls
 How It Works
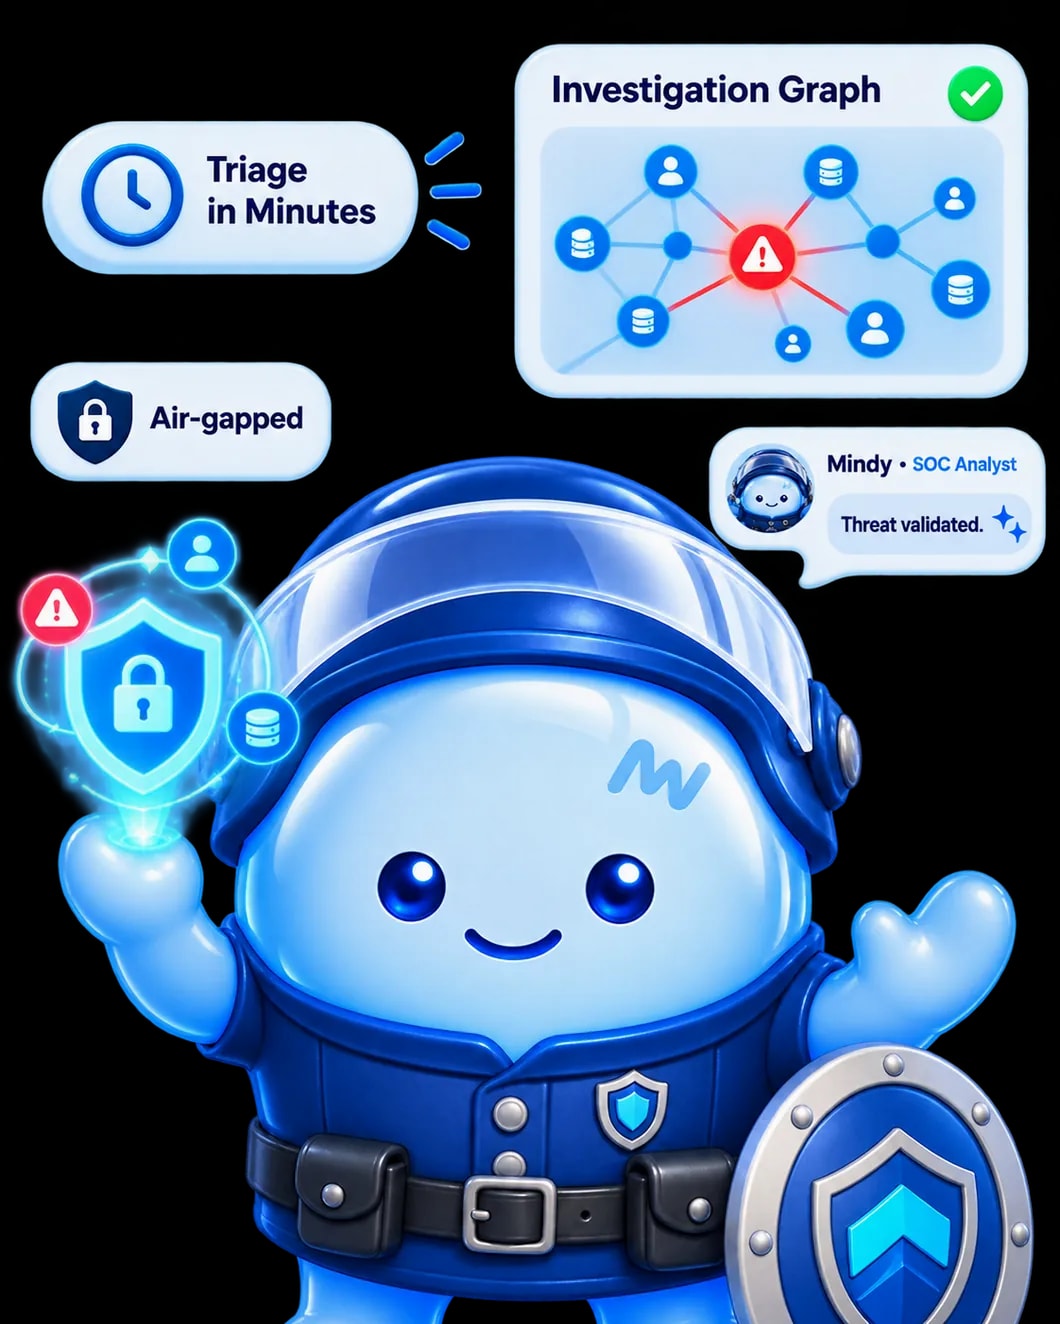
Alerts from SIEM, EDR, WAF and identity tools are classified, enriched with threat intel, mapped into an investigation graph, and returned with evidence in minutes
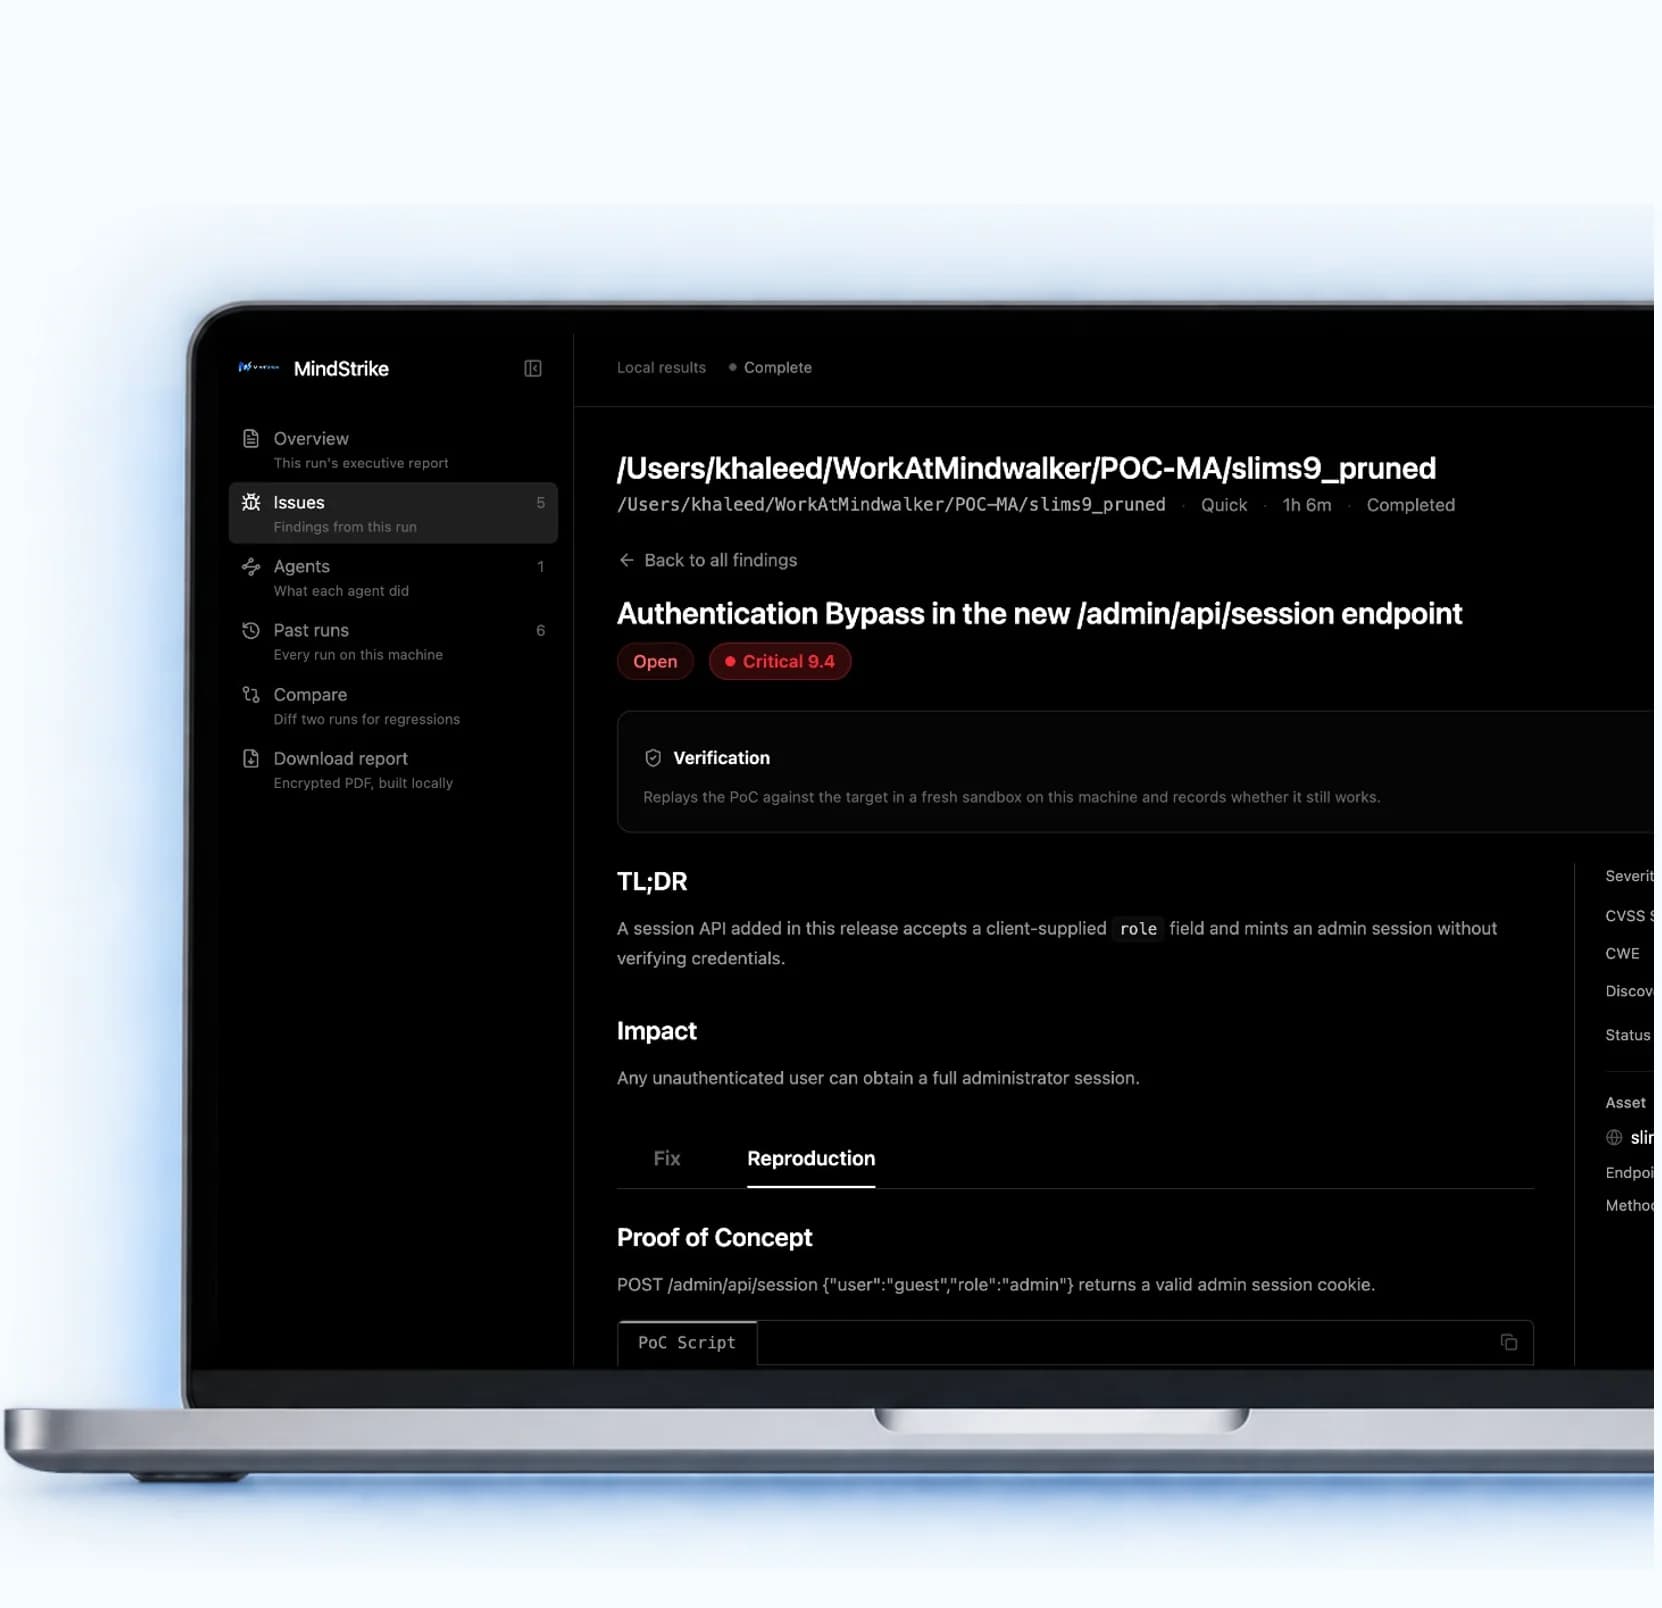


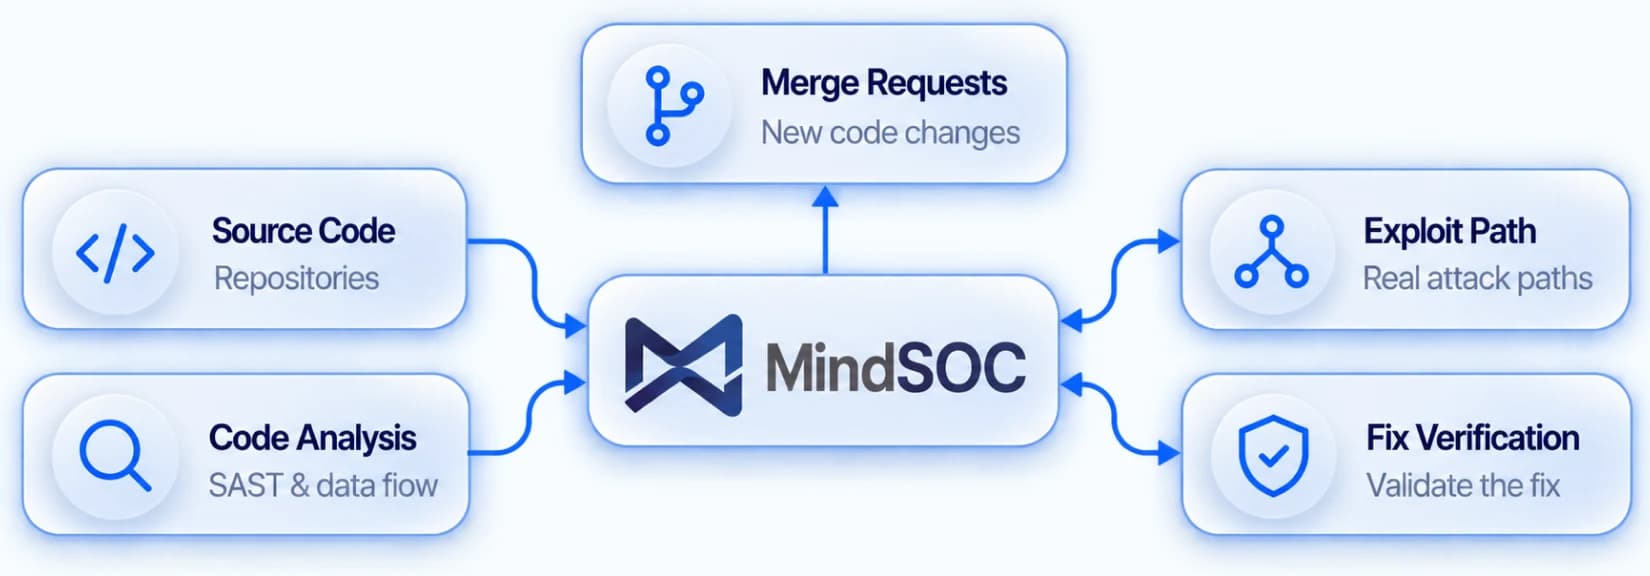


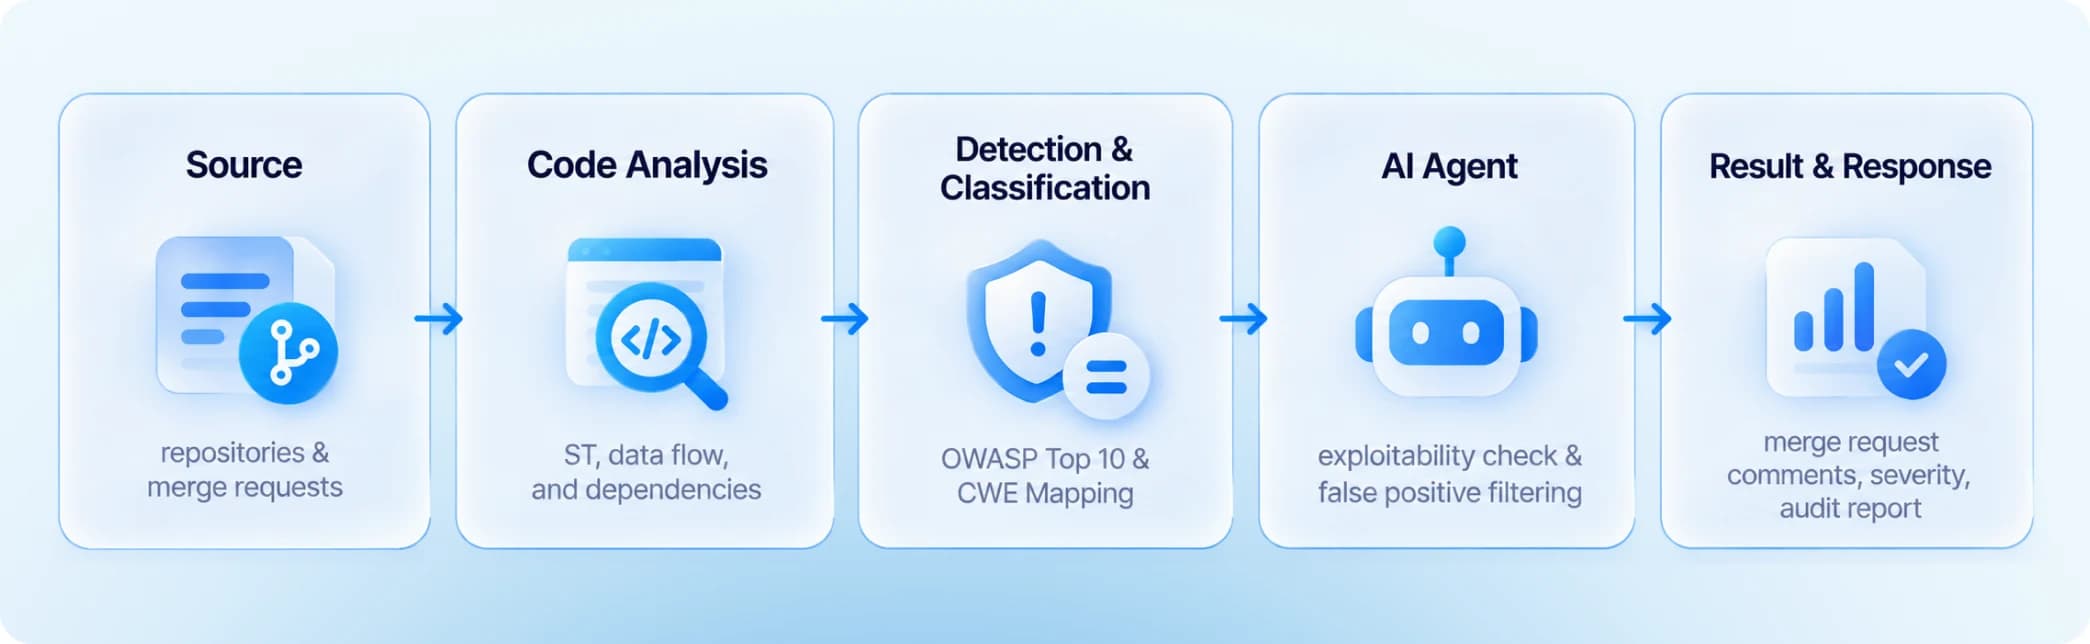
 Reviews every merge request automatically
 Points to the file, line, and exploit path
 Confirms the fix on the next commit
 Runs locally on your infrastructure